Authentication & Session Security
TOTP-based two-factor authentication, OTP-based password reset, brute-force lockout, and a session registry with per-device revoke. Support impersonation always requires a reason and gets tagged for audit.
Security settings with 2FA setup and active sessions
What you get
- 2FA (TOTP) with a pending-verification flow, not a password bypass
- OTP password reset revokes every active session on completion
- Super-admin impersonation is time-boxed, reason-logged, and visibly banner-flagged
More in Security
Related capabilities in the same part of Travix Cloud.
Access Management
Enterprise-grade IAM with RBAC and ABAC — 13 system role templates, a hierarchical permission catalog, teams, branches, data scopes, a session registry, and a policy engine with real financial guardrails.
User & Role Management
Day-to-day user admin — invite, deactivate, reset passwords, assign roles — kept separate from the bigger Access Management module, so small teams get a fast, focused screen instead of an enterprise console.
Branch Management
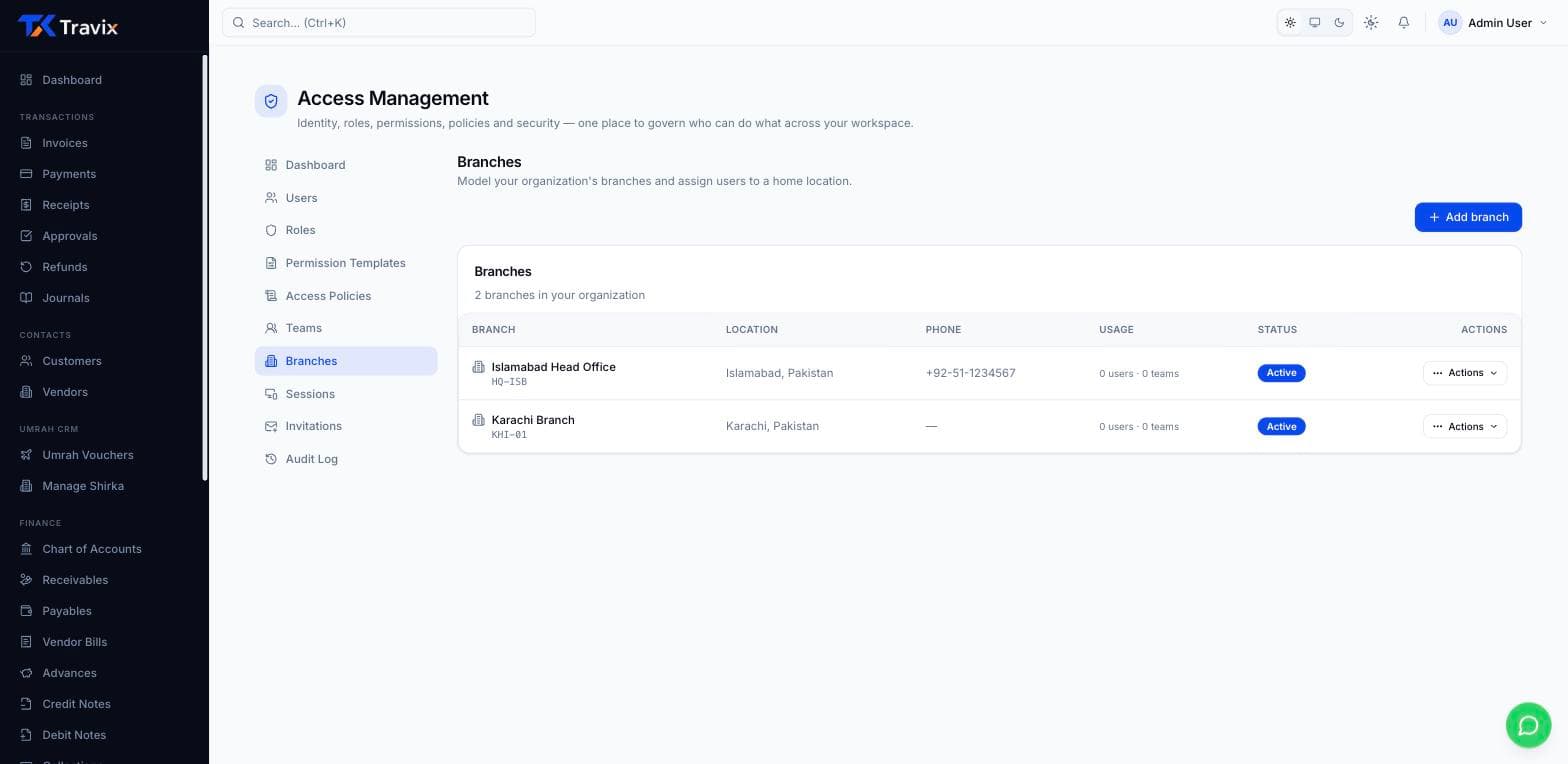
Model your organization as a branch hierarchy with an exclusive head office, give each user a home branch, and let multi-branch staff switch locations for the session without ever logging out. Vouchers, customers, and reports all carry a branch, so operations and reporting stay location-aware.
Multi-Tenant Security
Every table carries a tenantId. Isolation gets enforced at the middleware, repository, and guard layers — cross-tenant access isn't just discouraged, it's architecturally prevented.
Ready to run your agency on one ledger?
Join the travel businesses that traded spreadsheets and legacy ERP for a platform actually built around how agencies work.